At GTC Berlin on 21 October 2026, Jensen Huang stopped the product tour to say the agent has to be secure before it is useful. An agent is an autonomous system with access to files, networks and tools. The privileges you give it should be minimal, and you have to watch it. NVIDIA's answer on stage was OpenShell, with Sentry on BlueField-4 as the hardware monitor. This article is the request path, in the order the keynote and NVIDIA's own reference-architecture note describe it.
Why a prompt is not a control
The film Huang played made the point without a metaphor left over. Enterprises expect to deploy large numbers of agents. To be useful, those agents will reason, plan, use tools, read data and work together. The only thing stopping one from misusing that access, the film said, has been asking it nicely: please do not delete anything, please do not push to main, please do not touch the SSH keys. Huang's line after the film: hope is not security. Safety is engineering.
OpenShell is that engineering at the operating-system boundary. You write a policy for what each agent may touch. OpenShell enforces it at the level of system calls, file access and network connections. A proposed policy change is checked, by formal verification, against a permission ceiling, so an edit cannot quietly grant more than you intended.
The browser analogy in the film is the right one. Early web pages could do too much until the browser refused. OpenShell is the same move for agents. The refusal happens outside the model. A guardrail inside the prompt is not the control.
The path of one outbound call
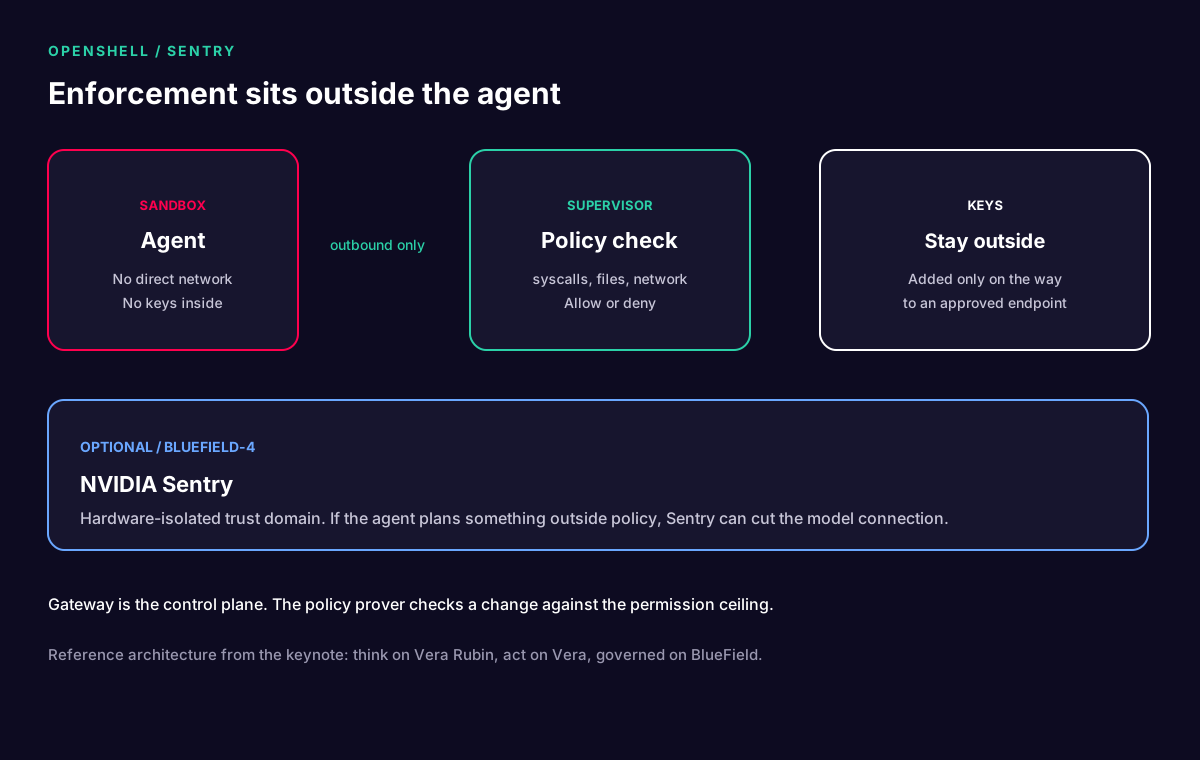
Every agent runs in its own sandbox. The sandbox has no direct route to the network. Every outbound request goes to a supervisor outside the sandbox. The supervisor checks the action against policy. If it is not allowed, it is denied.
Keys stay with the supervisor. They are added only on the way to an approved endpoint. A compromised agent cannot leak a key it never held.
Four roles, as the film named them:
- Gateway. The control plane.
- Supervisor. Makes the allow or deny decision.
- Sandbox. Holds the agent.
- Policy prover. Checks a proposed policy against the permission ceiling.
Sentry, off the host the agent can see
OpenShell itself is Linux kernel isolation plus runtime policy. Sentry is optional and sits further out. It runs on NVIDIA BlueField-4, in a hardware-isolated trust domain, on the path between the agent and the model. NVIDIA's technical post says BlueField-4 sits in the I/O path between agents running on Vera and the models they call. Sentry, built on DOCA, watches that path.
Because the reasoning traffic passes through Sentry, a plan that leaves policy can be stopped by cutting the connection to the model. Huang said that quarantine happens in milliseconds. Sentry also keeps tamper-evident records for detection, investigation and response. It does not rely on the agent reporting on itself.
NVIDIA's newsroom adds two figures we are not re-measuring: Sentry on BlueField-4 can raise agent capacity by up to 20 percent, because the security work is off the host, and a quarantine happens in milliseconds. Treat both as NVIDIA's claims.
Think, act, govern
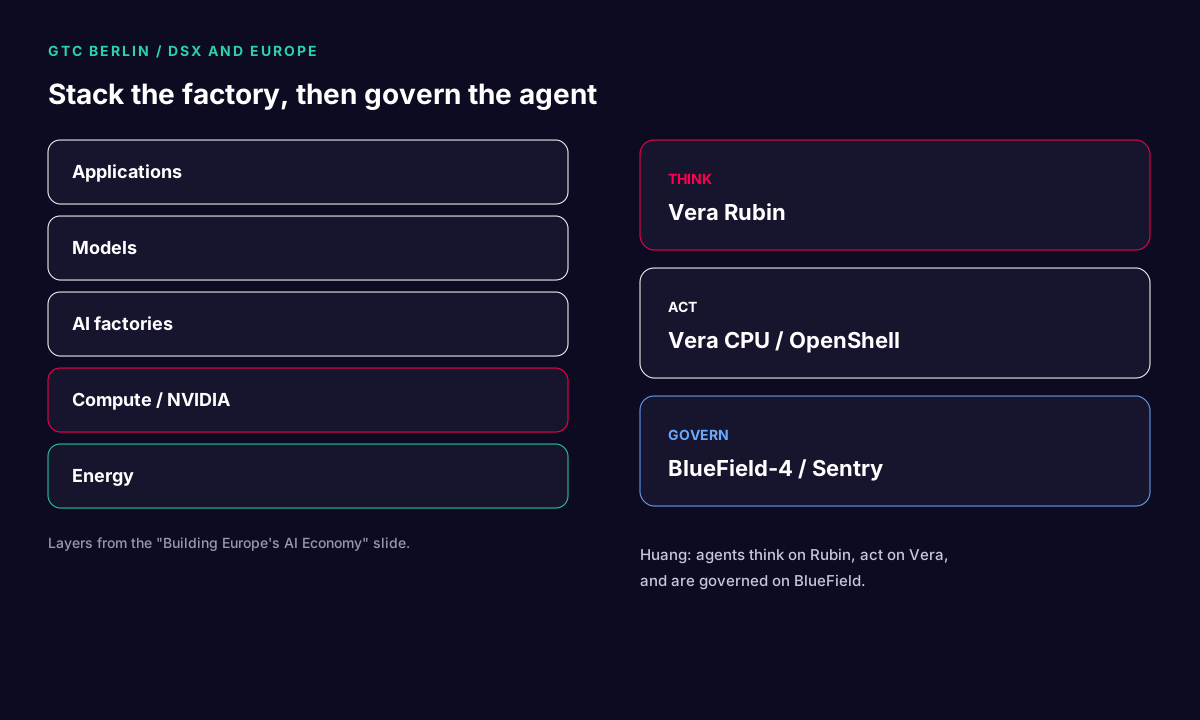
The reference architecture announced the same day puts three computers under those jobs.
- Vera Rubin runs the models, including closed models and open models built with Nemotron. NVIDIA says Vera Rubin NVL72 is usable for pre-training, post-training and inference, and quotes 30 times the throughput per megawatt on agent workloads. That number is theirs.
- Vera CPUs run the harness and the tools, inside OpenShell. NVIDIA says Vera delivers twice the performance of x86 at better efficiency. Again, their figure.
- BlueField-4 runs Sentry.
Huang's sentence in the press note: agents can think on Rubin, act on Vera, and be governed on BlueField. The same software stack is described as reaching the edge on RTX Spark, DGX Spark and DGX Station, and as running on Canonical, SUSE, Red Hat, and on Microsoft Windows with Microsoft Execution Containers. Cloud operating systems from AWS, Google Cloud and Azure are on the same list.
Privileges change every launch
Huang spent a minute on why a static allow-list fails. Every task, every person and every capability wants a different privilege. Every launch is different. Policy, enforcement and monitoring have to be dynamic. That is the part he called revolutionary: not one sandbox image for the company, but a policy decided when that agent starts.
He also said the point is not only that model vendors use OpenShell when they host agents. Companies receiving those agents need the same runtime, so an agent can run inside the company without inheriting the company's entire network.
Harnesses, and the Anthropic line
OpenShell is the sandbox. The harness is whatever you put in it. Huang named OpenClaw, Hermes and OpenHands, plus harnesses from LangChain and Deep Agents, or Python you write yourself. The published transcript of the keynote says Anthropic and NVIDIA are partnering "to create cloud OpenShell agents," and he pointed at a write-up on the website. We are not expanding that into a product name he did not use.
The software is open source under the Apache 2.0 licence, he said, and it runs from edge to cloud. Adoption, in the film, is two commands: install the CLI, create a sandbox, run the agent you already use. Our earlier note on running that CLI on Mac Studio and on NVIDIA Linux is the operator view. This article is the Berlin architecture around it.
Who NVIDIA named
The 21 October newsroom lists companies working with the reference architecture. We are repeating their list, not adding to it. Operating systems and clouds: Canonical, SUSE, Red Hat, Microsoft, AWS, Google Cloud, Azure. Model builders: Anthropic, Cohere, Google, Meta, OpenAI, Perplexity, Reflection, SpaceX Super Intelligence. Security: 1Password, Check Point, CrowdStrike, Cisco, F5, Fortinet, Microsoft, Okta, Palo Alto Networks, TrendAI, Zscaler. Banks exploring it: BBVA and Santander. Enterprise software: Cadence, Dassault Systèmes, IBM, SAP, Siemens, Synopsys, and Palantir with customers in production. SAP is connecting it to Joule Studio. ServiceNow said Arc, its long-running agent, is governed by the ServiceNow Super Intelligence Control Tower and enforced by OpenShell, with AI Passport carrying policy to OpenShell and Sentry. System builders: Dell, Cisco, HPE, Lenovo, Supermicro. Neoclouds and hosts: CoreWeave, Crusoe, Firebird, Firmus, GMI Cloud, IREN, Lambda, Nebius, Nscale, Oracle Cloud Infrastructure, Vultr. Inference and post-training: Baseten, Deep Infra, Fireworks, Together AI.
NVIDIA's own caveat sits under that list. Many products and features remain on a when-and-if-available basis. A logo on a slide is not a shipping integration you can order on Monday.
What to configure, in order
The film's "two commands" are the start, not the operating model. A team that will leave agents running should do the following, and stop if a step has no owner.
- Name the harness. OpenClaw, Hermes, OpenHands, or your own. One sandbox image per harness family is enough to start.
- Write the smallest policy that lets today's task finish. Files it may read. Hosts it may call. Tools that are read-only versus tools that write.
- Put secrets in the supervisor, not in the prompt and not in the image.
- Run one hostile test: a prompt that asks the agent to read a key, open a new host, or delete a file outside the allow-list. The deny must come from the supervisor, not from the model refusing in prose.
- Only then add Sentry if you have BlueField-4 on the path to the model. Without that DPU, OpenShell is still the control. Sentry is the extra seatbelt NVIDIA described, not a requirement for the CLI.
Dynamic policy is the part that will hurt if you treat OpenShell as a single company-wide allow-list. Huang said every launch can need a different privilege. That means the policy is an input to the launch, versioned next to the task, not a wiki page from March.
How this differs from a guardrail
A guardrail looks at text. It can miss a tool call that is polite and still destructive. OpenShell looks at the call the operating system is about to make. Both can be on. They are not substitutes. NVIDIA's own cybersecurity portfolio, which we have written up separately, still includes Nemotron Safety and NeMo Guardrails. Berlin's point was that those are not sufficient once the agent has a shell.
Edge systems get the same story at a smaller size. The newsroom names RTX Spark, DGX Spark and DGX Station as places the reference architecture extends. A desk machine can run the sandbox. It will not run Vera Rubin NVL72. Do not buy a workstation and describe it as an AI factory.
Sources
- Keynote transcript, SB61112: nvidia.com/on-demand
- Newsroom, 21 October 2026: OpenShell Reference Architecture
- Technical post: How OpenShell secures agent workloads
- OpenShell project: github.com/NVIDIA/OpenShell