This is the long-form deep dive. For a shorter skim, see the companion blog. Related: agentic AI security · AI Healthcare.
1. From pilots to action-taking agents
Healthcare teams are moving past AI pilots. The new wave of AI agents does much more than answer questions. An agent can work out what a patient wants, pick the right tool, connect to other systems and take action. It can book appointments, answer billing questions, take payments and support clinical workflows.
This brings a new kind of security problem. Normal software follows a fixed path. An AI agent does not. It decides the next step based on the conversation and how the patient responds. The path can change in real time. When that agent works close to Protected Health Information (PHI) or payment data, the key question is not “Is this AI safe enough to see sensitive data?”
The better question is: What access does the agent actually need to finish the patient’s request?
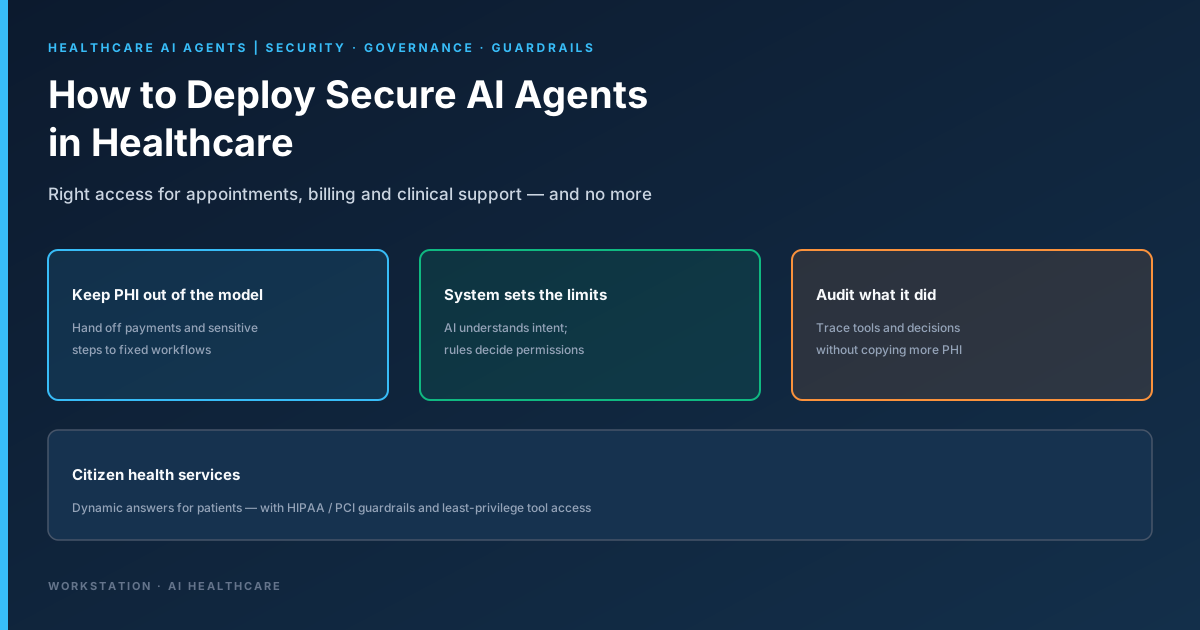
Below are three design ideas Workstation recommends for healthcare leaders, clinical operations, security and compliance teams — including programmes that inform citizens dynamically at national or regional scale.
2. Keep sensitive data away from the AI
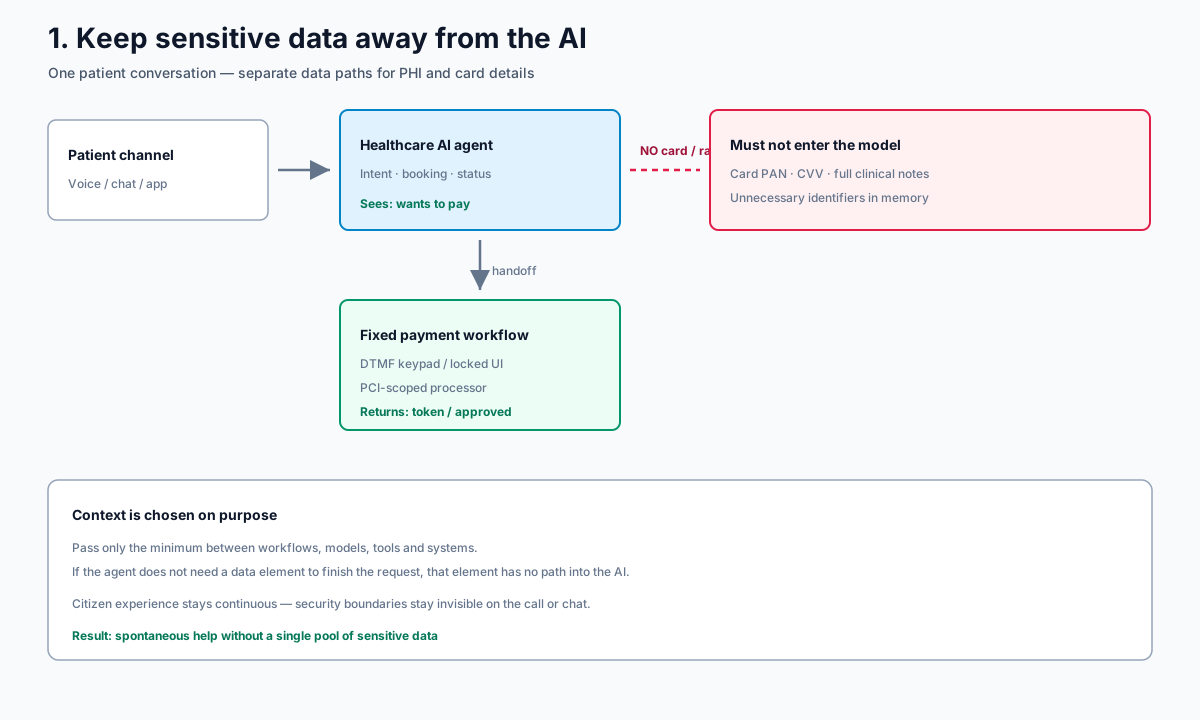
Picture a patient calling about an unpaid bill. In one call, they might mention a procedure, share personal details and read out a card number.
For the patient, it is one conversation. For the system, it should not be one pool of data.
The agent needs to know that the patient wants to pay, and whether the payment worked. It does not need to see the card number.
Sensitive steps should be handed off to separate, fixed workflows:
- On a phone call, this could be secure keypad entry (DTMF), where the patient types their card details and the AI never hears them.
- In digital channels, this could be a separate, locked-down payment flow.
The sensitive data goes straight to the system built to handle it. The agent only gets back what it needs to carry on, such as a token or a “payment approved” status. The patient notices nothing. They are still on the same call or in the same chat.
This idea goes beyond payments. If the agent does not need a piece of sensitive data, that data should have no path into the AI at all.
This also applies to context and memory. An agent needs context to give the patient a smooth experience. But context must not turn into a back door for data leaks. Your design should control what moves between workflows, models, tools and other systems, so that PHI, personal data and card data do not follow the conversation into places they do not belong.
Context should be chosen on purpose, not passed along by default.
2.1 Practical patterns
| Channel | Agent may see | Must stay outside the model |
|---|---|---|
| Voice bill pay | Intent, balance summary token, approval status | PAN, CVV, full card readback |
| Appointment booking | Slot options, clinic rules, confirmation IDs | Full chart browse, unrelated diagnoses |
| Clinical support | Purpose-bound sections, allowlisted tools | Unbounded EHR search, export dumps |
| Citizen guidance | Public health feeds, aggregated capacity | Identifiable case lists without legal basis |
3. Do not use the AI as your security guard
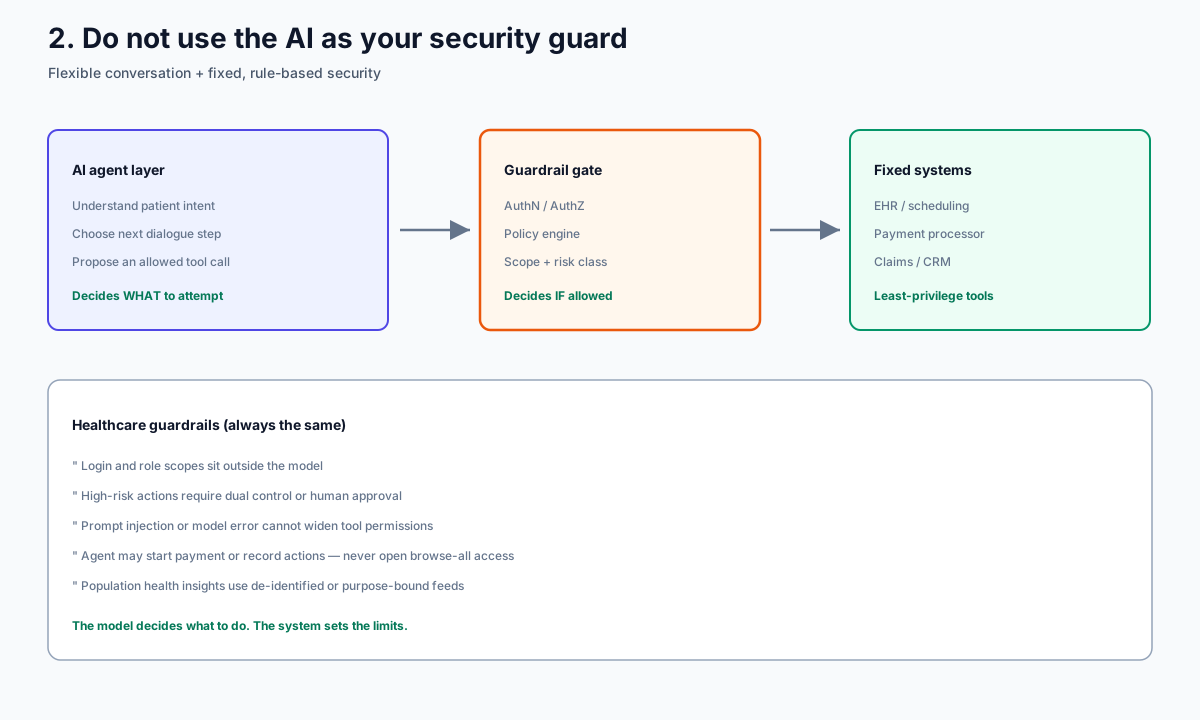
AI is useful because it understands language and responds in a flexible way. Those same traits make it a poor place to enforce security rules.
A simple rule of thumb:
- Let the AI work out what the patient wants.
- Do not let the AI decide what it is allowed to do.
The strongest setup pairs a flexible conversation with fixed, rule-based security. Login, permissions, handling of sensitive data and high-risk actions should all sit behind controls that always behave the same way.
For example:
- The agent can start an approved payment flow without ever seeing card details.
- The agent can request an allowed action in the patient record system without getting open access to all records.
This also limits the damage when things go wrong. An agent might be tricked by a bad prompt, get mixed signals or simply make a mistake. When that happens, your system design, not the model’s judgment, should decide how far the mistake can spread.
The model decides what to do. The system sets the limits.
The aim is not to make an agent trustworthy enough to access everything. It is to build a setup where the agent never needs access to everything in the first place.
3.1 Guardrail checklist
- Identity of the human (or service account) is established before tool use.
- Each tool has an allowlist, purpose, and risk class.
- Write actions (orders, payments, record updates) require policy gates or human approval.
- Prompt injection cannot escalate scopes — scopes live in the control plane.
- Secrets for tools come from short-lived leases (for example HashiCorp Vault), not chat memory.
Workstation’s broader patterns for MCP OAuth, private networking and Vault leases are documented in the agentic AI security brief.
4. Track what the agent did, not just what it said
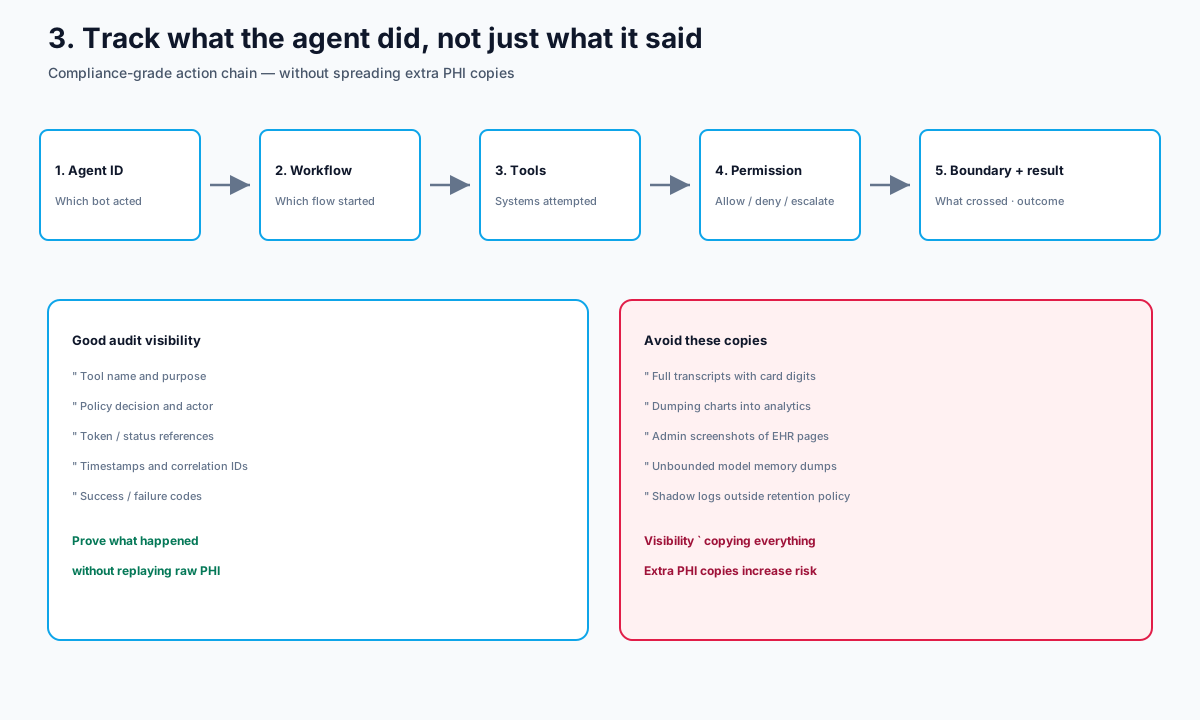
A transcript shows what the patient and the AI said. It does not always show what the agent actually did. For compliance teams, that gap matters a lot.
A good audit trail for AI agents should show the full chain of actions:
- Which agent acted
- Which workflow it started
- Which tools and systems it tried to use
- What permission decision was made
- What data crossed a boundary
- What the result was
This does not mean saving every bit of PHI the agent came across. Copying sensitive data into transcripts, logs, analytics tools and admin systems creates the very risk you are trying to avoid.
Good visibility is not about recording everything. It is about being able to prove what happened without making extra copies of sensitive data.
5. Citizen health: spontaneous information with strong protection
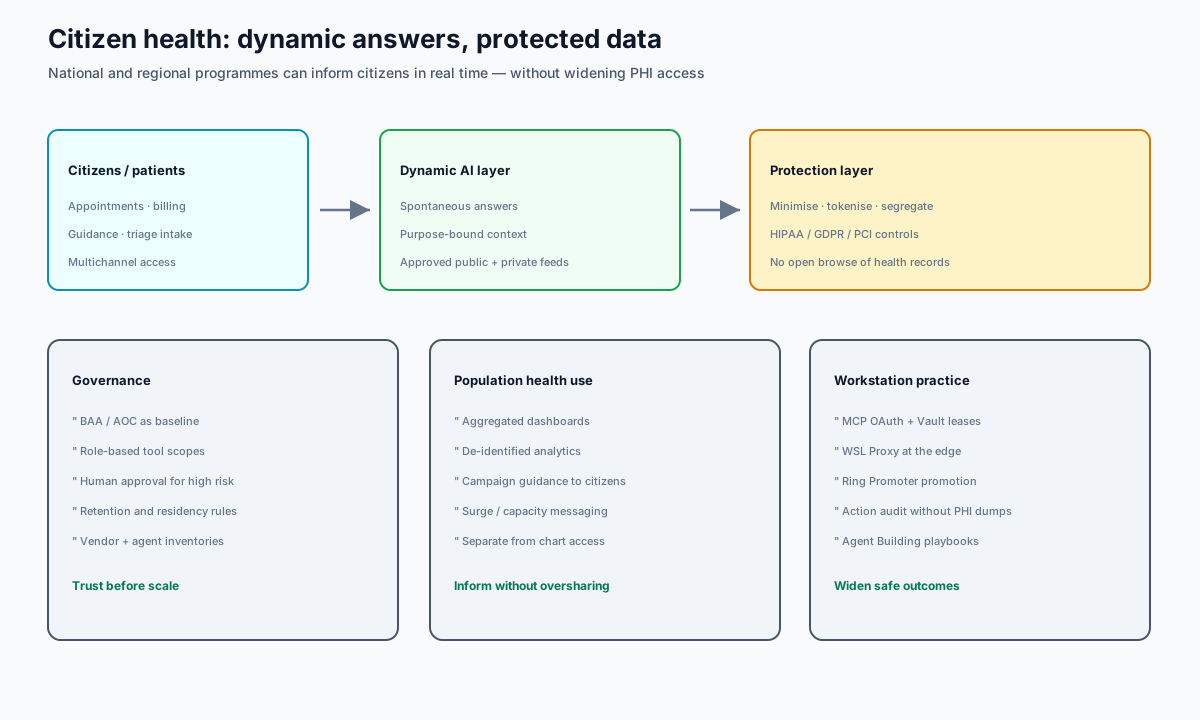
Governments and health systems increasingly want agents that can answer citizens dynamically — clinic hours, booking, vaccination guidance, capacity messages — while protecting individual health records.
That requires two planes:
- Dynamic experience plane — language, dialogue, and approved content feeds that feel spontaneous.
- Protection plane — minimisation, tokenisation, purpose limitation, residency, retention, and segregating identifiable records from population dashboards.
Population health analytics should prefer aggregated or de-identified data. Campaign messaging to citizens should not become a side channel into chart access. The same three principles apply: separate sensitive paths, enforce permissions outside the model, and audit actions without PHI sprawl.
6. Build for trust first. Then scale.
When choosing a technology partner, a Business Associate Agreement (BAA) for HIPAA and an Attestation of Compliance (AOC) for PCI DSS are important starting points. But paperwork alone does not answer the questions that matter most:
- What can the AI agent see?
- What can it do?
- What happens when it gets something wrong?
Healthcare teams that want to grow their use of AI should:
- Keep the AI conversation separate from sensitive data.
- Put fixed, rule-based controls around the AI’s flexible decisions.
- Make every agent action easy to trace, without spreading sensitive data further.
Instead of asking whether an agent can be trusted with more access, you can give agents more abilities while keeping strong guardrails in place.
That is how healthcare AI grows safely: not by widening what the AI can see, but by widening what it can safely get done.
7. How Workstation helps
| Capability | Role in healthcare agent programmes |
|---|---|
| Agent Building | Map intents to tools with approval gates and least privilege |
| MCP OAuth + Vault | Short-lived secrets and identity-bound tool access |
| WSL Proxy | Edge control for agent HTTP paths |
| Ring Promoter | Health-gated promotion of agent changes through environments |
| AI Healthcare | Sector solutions and operating model |
8. Closing
Secure healthcare agents are a systems problem more than a model problem. Separate the conversation from sensitive payloads, keep permission decisions deterministic, and audit outcomes without cloning PHI into every log store. Do that, and you can still deliver spontaneous, dynamic support for patients and citizens — with guardrails that hold when the model makes a mistake.
Published by Workstation. Contact: /en/contact-us.